
Organisations are buried under the current explosion of data and the increasing cost of managing, storing and using telemetry data, both of which can cause lags in detection and response times. It becomes harder to identify issues, access the right data to make decisions, and come to a resolution quickly.
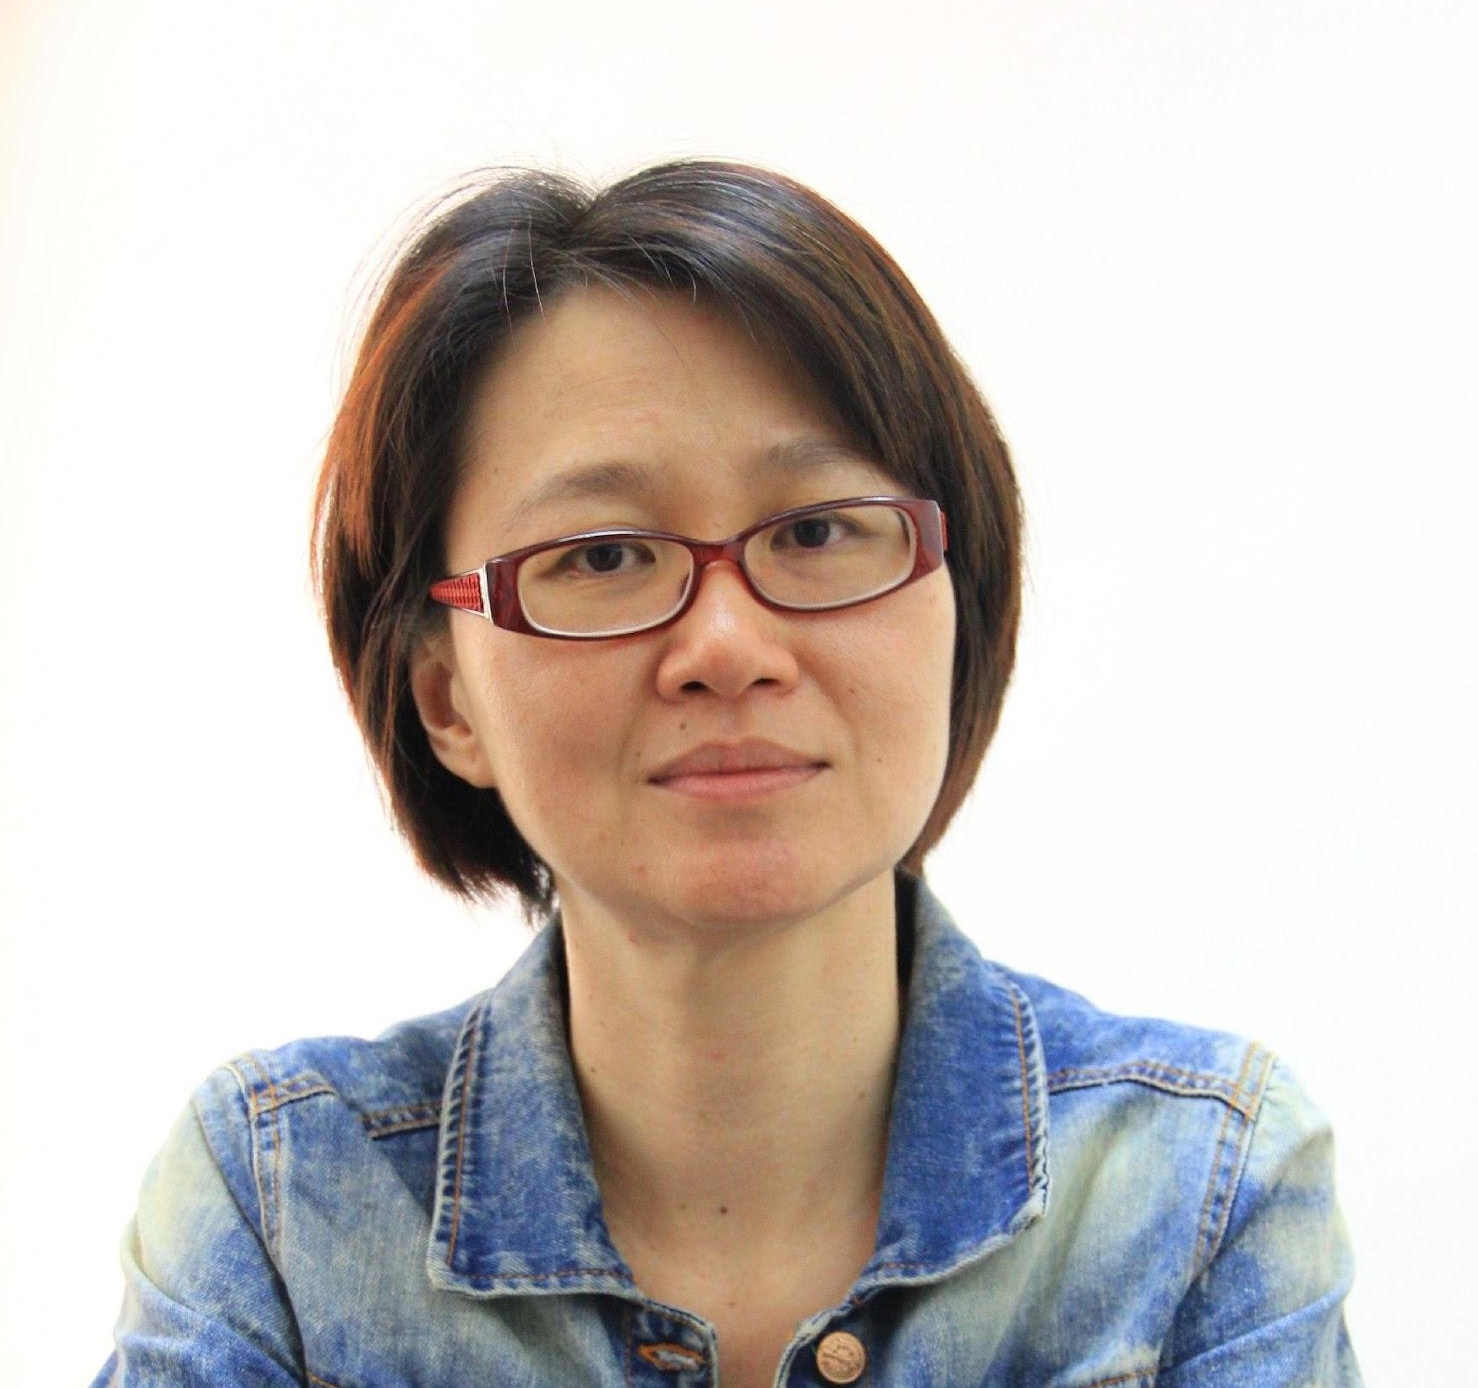
At the sidelines of Splunk’s Leadership Forum in Singapore, Robert Pizzari, Group Vice President, for Splunk’s APAC strategic advisory organisation, had a conversation with Enterprise IT News about the growing complexities of cybersecurity compounded by “an absolute downward economic pressure within organisations to become more operationally efficient and effective.”
New data practices
Clicking into a Splunk 2025 report about the new rules of data management, he talked about how one of the levers that can be applied to accelerate efficiency and efficacy objectives, is being deliberate around data. “(Using data) when we need it versus just dumping everything into Splunk, for example. So, a very deliberate and intentional strategy around assessing data, with the objective of giving organisations greater flexibility.”
In this regard, he was referring to three data practices that facilitate value creation for an organisation, like data quality, data reuse, and data tiering. For example, deploying a data management pipeline with these three rules, can lead to a cleaner data set.
There are significant opportunities for customers to take advantage of, particularly those that have got Cisco real estate and technologies in their environments, in the areas of data analytics, or cyber operations and observability.
Robert Pizzari
“Then I can train the models to help practitioners in cybersecurity or observability make better informed decisions, because it is being trained on my data within my environment.” Robert explained, adding that there needs to be a human in the loop to supervise the output and refine the way that the model is being trained, because using publicly available AI models may lead to inaccuracies.
Splunk itself focuses on integrating and customising AI models rather than creating them from scratch. “Splunk is not building large language models…we will take open source models and integrate them into Splunk, assess that they’re safe, reliable, and do our own training,” the VP said.
Cybersecurity and observability domains
According to Robert, the power of what Splunk does for an organisation is that it will help with cross correlation – collecting log data coming from IT systems, applications, physical hardware, network, security devices, controls, users, authentication logs.
This capability can be applied to the cybersecurity domain – providing a degree of real-time monitoring and visibility of the IT estate and the organisation’s crown jewels – but it is also powerful in the observability domain – focusing on application availability and performance.
“Can you imagine how an entire economy can be disrupted if a major banking service goes down for a day here in Singapore, can you imagine the disruption to transportation, to food and beverage, to hospitality?” Robert posed the hypothetical question.
Third party vulnerabilities
According to the WEF Global Cybersecurity Report, concerns about software vulnerabilities, supply chain cyberattacks and limited visibility into third-party security are increasing, with 48% of Chief Information Security Officers (CISOs) reporting difficulties in enforcing security standards and managing the risks associated with reliance on critical providers.
Robert said, “What we’ve seen more recently in cybersecurity is that there have been supply chain attacks… that third party providers can have access to my internal systems to run their maintenance routines, for example. So, I have to monitor them.”
Organisations are operating in a continuously evolving landscape where vulnerabilities can emerge from direct internal threats as well as from an extended ecosystem of service providers and partners. Organisations needing to carefully monitor third-party access and also assess the security practices of external service providers, cannot be emphasised enough.
Also critical for organisations to implement, is robust monitoring and access controls for third-party interactions, a capability which Splunk is building as it is now part of a larger organisation, Cisco.
Robert concluded, “There are significant opportunities for customers to take advantage of, particularly those that have got Cisco real estate and technologies in their environments, in the areas of data analytics, or cyber operations and observability. Together with Splunk, there is a broader capability around monitoring and cybersecurity applying analytics, as well as AI assistance and agentic technologies.”