Join our community and be part of the conversation.
To subscribe, simply enter your email address on our website or click the subscribe button below. Don't worry, we respect your privacy and won't spam your inbox. Your information is safe with us.
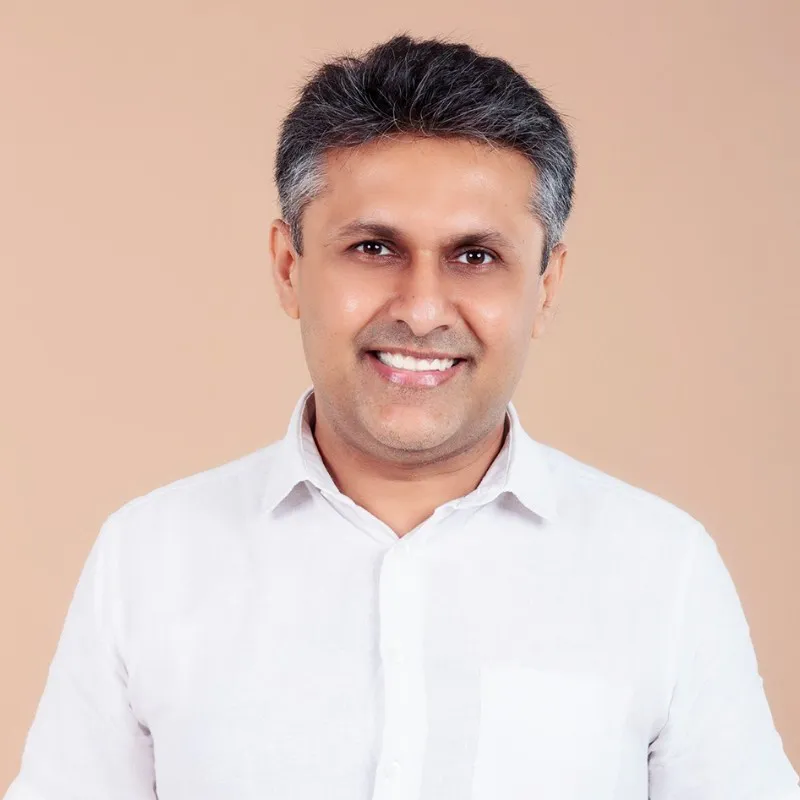
During an interview at the sidelines of GovWare 2026 in Singapore, Palo Alto Networks’ VP in ASEAN, Haji Munshi, described a cybersecurity landscape characterised by AI-assisted and autonomous attacks, a rising number of vulnerabilities, and the complexity of enterprise security tools. His prescription? More visibility, faster response and a broader shift toward AI-enabled security operations.
Haji Munshi
AI-powered attacks were a central concern raised by Haji and he pointed to what he called the “Hugging Face incident,” describing it as an example of hundreds of agents working together in a sophisticated cyberattack. For enterprise security leaders, he said, the concern extends to closed AI models and also “open models that are becoming as proficient in terms of executing those types of attacks.”
He added, “I think that is a consistent theme over the last three days (at GovWare2026) which Is how do you deal with these types of very sophisticated attacks being orchestrated with support from agents (or agent-assisted), but now increasingly more agent (being) fully autonomous.”
Agent attack – assisted or autonomous
“I think it’s quite real,” Haji said, describing the prospect of agent-assisted – and increasingly autonomous – attacks. He said customers were looking for ways to gain visibility into agents in their enterprises, understand their access, and distinguish agentic traffic from human traffic.
A surge in vulnerabilities that AI systems may uncover is also worrisome with tests revealing frontier models having only 10-percent overlap in vulnerability discovery. “They’re finding very distinct and unique vulnerabilities, and so we know that there is going to continue to be a deluge of vulnerabilities that are going to be uncovered.”
He cited a projection that more than 66,000 CVEs could be released in a year, while noting that organisations may struggle to patch at that pace.
One response he described is not a new topic – virtual patching – which uses security signatures to help block exploitation while customers work through remediation. Haji said Palo Alto Networks had used frontier models to identify vulnerabilities in open source packages before they became publicly known.
It’s also about being able to make detections with high fidelity, low false positives, and then to be able to respond to them and to be able to go after them.
Haji Munshi
“We’ve had access to most of these frontier models for much longer than most other providers of security equipment in this industry, and so we’ve had a chance to actually use those models to be able to do our own vulnerability testing – we’ve uncovered 14,000, 15,000 over a few weeks, and having that visibility before it becomes publicly known allows us to be able to build a signature within our product, so that we can stop those type of vulnerabilities being exploited.”
Visibility across agents and identities
As companies adopt AI internally the risks are not limited to external attackers. Employees and “citizen developers” may introduce tools or agents that IT teams have not fully monitored. He described Palo Alto Networks’ acquisition of Koi as a way to monitor agents on endpoints, including their privileges and data access.
Haji said, “That product actually sits on an endpoint and is able to monitor at the software layer all the agents that are in the device and their privileges. It can answer questions like what access do they have in terms of data, and whether there is a need to be able to stop that.”
There is a very strong likelihood that our customers will need to transform how they think about SOC operations.
Haji Munshi
He also pointed to an agentic gateway approach, via their PortKey acquisition, which he said is intended to route agent traffic through a central point for visibility and control. Identity is another concern due to the growth rate of machine identities compared to human identities; Haji cited a regional statistic of 111 machine/agent identities for every human one. All of these need to be managed alongside digital certificates to establish trust between systems.
These capabilities, he explained, need to fit into a wider security architecture rather than sit in isolation. “AI security has to be very comprehensive,” he said, naming the endpoint, security operations center, gateways and network visibility as parts of the picture.
Fight AI with AI
“We believe that we are at this watershed moment in the industry where our customers need to really think about how they want to transform how they think about their cybersecurity strategy. With machine speed attacks expected to escalate, Haji thinks it is not just about having alerts. “It’s also about being able to make detections with high fidelity, low false positives, and then to be able to respond to them and to be able to go after them.”
“Our genuine belief as a company is that we need AI to fight AI.” He also cited a distinction used by the company’s CIO that security teams should be “on the loop rather than in the loop”- overseeing and governing automated systems.
“There is a very strong likelihood that our customers will need to transform how they think about SOC operations.”
For Southeast Asia, Haji said Palo Alto Networks’ priorities include investing in technical and customer-facing teams, strengthening its partner ecosystem and providing packaged or managed service options for organisations without extensive in-house security capacity.
Haji observed that events like GovWare served as a really great melting pot for other countries to come together to “agree on policy … and align on the best way to share information and to collaborate.”
Singapore’s Senior Minister, K. Shanmugam had also leveraged his opening address to launch Singapore’s Cybersecurity Strategy 2026, outlining a shift towards more proactive cyber defence.
Haji noted, “One thing that I do find was also very well discussed was this belief … that nobody can do it on their own.”
Cat Yong is Editor-in-Chief of Enterprise IT News, a regional news website which began in Malaysia circa 2011. A common theme in all of her work - opinions, analysis, features and more - is how technology and innovation drives business and outcomes.
A career tech journalist for over 20 years.