Join our community and be part of the conversation.
To subscribe, simply enter your email address on our website or click the subscribe button below. Don't worry, we respect your privacy and won't spam your inbox. Your information is safe with us.
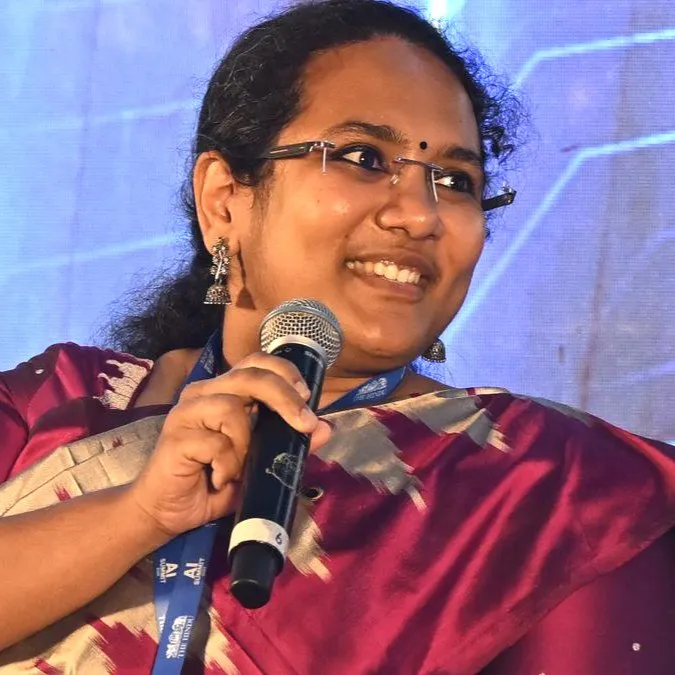
Malaysia’s planned sovereign AI cloud could give enterprises greater control over sensitive data and AI workloads, but an interview with Zoho Corporation reveals its head of AI security, Sujatha S. Iyer, stressing that locally governed infrastructure must be matched by strong access controls, clear accountability, and tested recovery planning.
Announced in Budget 2027, the initiative aims to keep citizens’ data and national strategic information under sovereign control. The budget identifies local regulator, the Malaysian Communications and Multimedia Commission (MCMC) as its developer.
Sujatha S. Iyer
For enterprises, the potential extends beyond local hosting. Sujatha also identifies three questions that can hold back AI deployment: where sensitive data is processed, who can access it, and which jurisdiction governs its handling.
“Establishing a locally governed infrastructure could give enterprises more control over these arrangements,” Sujatha said.
A bank, for example, could use AI to summarise customer documents within an approved local environment, subject to defined limits on provider access and data retention. Provider audit evidence could also offer a baseline for subsequent projects.
Sujatha frames sovereign infrastructure as a foundation for stronger governance, rather than a substitute for it. Enterprises would remain responsible for controlling access, monitoring activity and ensuring that AI applications handle information appropriately.
Bringing governance into everyday AI use
The policy push comes as Malaysia develops its proposed AI Governance Bill. In July, the Ministry of Digital launched stakeholder engagement on a risk-based framework that would distribute responsibilities according to each party’s role and level of control across the AI lifecycle. The proposed framework also encourages safeguards, incident reporting and AI sandboxes to support responsible innovation.
Within enterprises, Sujatha argued that governance should begin by addressing the conditions that encourage employees to use unapproved AI services.
“When approved tools are difficult to access or are disconnected from everyday work, employees may turn to external services and upload business information outside the organisation’s controls.”
Providing approved AI capabilities within existing workflows would give staff a practical alternative, supported by clear data-sharing boundaries and appropriate permissions.
As deployments expand beyond isolated pilots, Sujatha called for consistent oversight of employee and agent identities, data access and activity logs.
“Each agent needs a named owner and credentials limited to its authorised tasks, with access revoked when its purpose ends.”
Monitoring should also extend beyond the model to software dependencies, retrieved content and connected tools, helping teams investigate unusual data access or unauthorised actions.
Measuring value – and proving resilience
The Ministry of Health’s cloud-based clinic management system offers an example of measuring technology’s effectiveness through service outcomes. Health Minister Datuk Seri Dr. Dzulkefly Ahmad reported that 86.7-percent of patients were seeing a doctor within 60 minutes following the cloud technology’s implementation.
Cloud adoption must be viewed as an operational catalyst rather than just an infrastructural migration.
Sujatha S. Iyer
Sujatha’s responses draw a wider enterprise lesson from that experience: cloud investment should address operational bottlenecks and connect workflows, rather than simply relocate infrastructure.
For banks, that could mean reducing manual hand-offs in loan processing. For logistics operators, it could mean connecting warehouse events, vehicle movements and delivery confirmations so staff can intervene when shipments fall behind.
“Cloud adoption must be viewed as an operational catalyst rather than just an infrastructural migration.”
Ahead of 2027, Sujatha’s responses place equal emphasis on demonstrating resilience.
Enterprises should test what happens when a cloud dependency fails, an AI service becomes unavailable, or an agent’s access must be revoked, while ensuring that recovery planning maintains compliance.
Cost and performance should be assessed together. A surge in AI model API calls could reflect genuine demand, an application trapped in a retry loop, or compromised credentials. Connecting performance information with identity activity and security logs would help establish the real cause of a surge.
The proposed measure of maturity is therefore not the number of AI pilots or cloud workloads deployed, but whether service quality, security, recovery performance and cost per completed task demonstrate sustainable business value.